Stream
Technical Guides
Articles in this stream across the journal.
44
Articles published
Tue Nov 2026
27 Oct 2026 15 min read
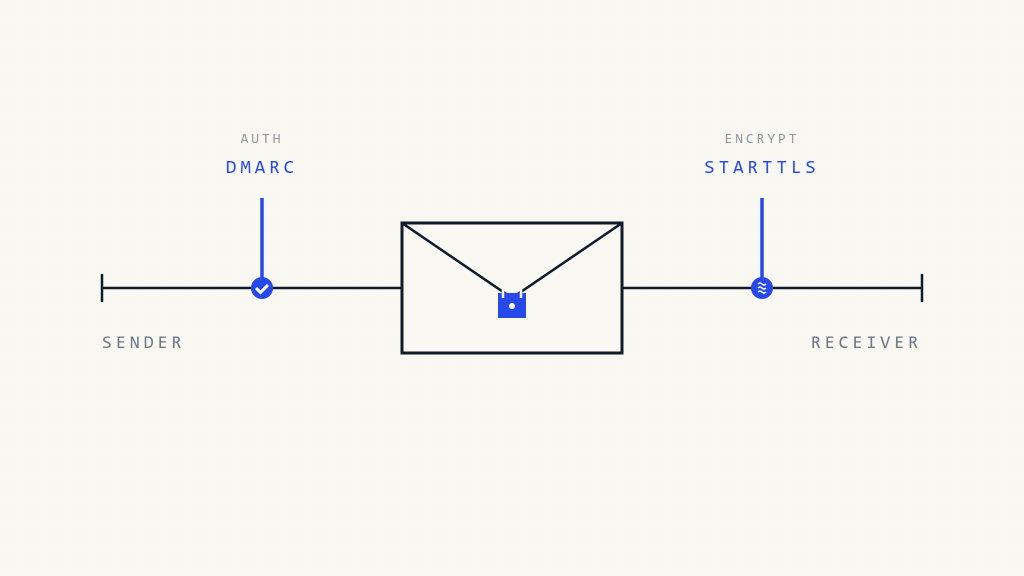
STARTTLS vs DMARC: Email Security Protocols Explained
STARTTLS encrypts email during transmission while DMARC authenticates sender identity. Learn how both protocols work together to prevent phishing and protect data in transit.
Read the article
Subdomain DMARC Inheritance: Debug Policy Gaps
Prevent subdomain takeover by correctly configuring DMARC inheritance. Learn where subdomain policies fail and how to close exploitable authentication gaps.
12 min 23 Oct 2026
Email Forwarding Breaks DMARC: Here’s Why
Email forwarding triggers DMARC failures because SPF and DKIM break when messages are relayed. Learn why forwarding causes authentication failures and how to implement forwarding-safe policies.
10 min 21 Oct 2026
DMARC Policy Evolution: When to Move from None to Quarantine to Reject in 2026
Strategic guide to DMARC policy enforcement progression from p=none to p=reject, including failure conditions, staging strategies, and validation timelines for 2026.
12 min 26 Aug 2026
VMC Certificates Explained: Your Complete Guide to Verified Mark Certificates
Master VMC certificates for BIMI implementation. Learn validation requirements, business impact, and implementation strategies for secure email brand authentication.
7 min 24 Aug 2026
SPF Record Limits: The Silent Deliverability Killer
The 10-DNS-lookup SPF limit breaks authentication for 63% of multi-vendor organizations. Learn how to count lookups, prevent permerror, and fix SPF before delivery fails.
13 min 13 Aug 2026
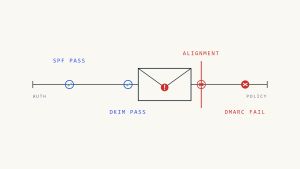
The Hidden Reason Authenticated Emails Still Fail
Authentication passes but emails still fail. Learn why DMARC alignment differs from SPF and DKIM passing, where alignment breaks, and what to verify beyond authentication.
9 min 12 Aug 2026
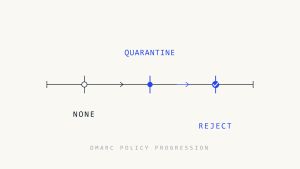
DMARC Reject Policy: When and How to Implement It Safely
Learn how to safely implement DMARC reject policy without breaking legitimate email. Practical guide to moving from quarantine to reject with validation steps and failure prevention.
12 min 13 Jul 2026
PCI DSS Email Security for E-commerce: Shopify and WooCommerce DMARC Setup Guide
Complete step-by-step guide for implementing email authentication on Shopify and WooCommerce to support PCI-DSS compliance requirements and protect e-commerce operations.
15 min 9 Jul 2026
How to Document Email Authentication for PCI-DSS Audits: A QSA-Ready Compliance Guide
Step-by-step guide to prepare DMARC documentation that satisfies QSA requirements for PCI-DSS compliance audits, including technical configs and process docs.
9 min 7 Jul 2026
AI DMARC Integration: How to Enable Intelligence Without Breaking Security Boundaries
Architectural guidance for secure AI integration in DMARC platforms using Model Context Protocol (MCP) to enable email security intelligence without expanding attack surfaces.
6 min 6 Jul 2026
DMARC p=none Explained: Monitoring Mode, Risks, and the Path to Enforcement
DMARC none policy enables authentication monitoring without enforcement. Learn when to use p=none, common failure modes, and how to advance to quarantine or reject policies safely.
10 min 23 Jun 2026
DMARC for Payment Processors: Supporting PCI DSS Anti-Phishing Controls
Complete guide to implementing DMARC email authentication for payment processors, including PCI-DSS compliance considerations and MTA-STS integration.
12 min 22 Jun 2026
The Skysnag Scanner
Check your domain's DMARC compliance.
Five protocols. Sixty seconds. No account. A full authentication-posture report on your domain, delivered before your coffee cools.
DMARC · SPF · DKIM BIMI · MTA-STS · TLS-RPT No signup required